
Samsung Group: 1TB Data Breach from Ransomware Attack
samsung.com
This victim has been identified as a duplicate of another entry in our database. However, this may not always be the case: the same organization can be targeted multiple times by the same or different ransomware groups, which may result in separate legitimate entries. Search for related entries
Description:
Infostealer activity detected by HudsonRock
Compromised Employees: 4382
Compromised Users: 2481605
Third Party Employee Credentials: 2163
External Attack Surface: 200
Infostealer Distribution
Exposure Report
by ParanoidLabFortiBleed Exposure Detected
This domain's FortiOS SSL-VPN credentials were exposed via the "FortiBleed" leak (CVE-2022-40684), including the FortiBleed 2.0 leak from October 2026.
DNS Records:
The following DNS records were found for the victim's domain.
- abusewhois.co.kr
- ssdomainsamsung.com
- mailin.samsung.com.
- smartsheet-site-validation=E2jBYaDqtbMgG1u9Jzz2eQBNGVL2eea-
- globalsign-domain-verification=BD8E0953267AFCAEF59AFBF5F00BEB67
- pardot1061372=cd7a8dc7dac11576e3160df3645c3be60beb48d38262fe75e1b83b6ed4547e2f
- pardot1061372=4fedddc5665b4f323efd74d4970852e6a46f8df316987974967da26bef35bf24
- google-site-verification=If15ip-WHY67QHEaM6ka9WKCcxgFHbS1oaXJswpUbHQ
- google-site-verification=2Qn3FwdHxOdx-U2EBlX2Aq6OPFHM-JGRpo5fN2vEr88
- google-site-verification=4pYi1ZoA5M9sNwJ39mlfRLPA5w_J2lqCVFEVUPyojp8
- pardot848313=56b423327c6bbcc73c4888f1e7a74aa35be107baa0d8dbc0d60d3078016cdedb
- asv=bbc7c9d6c4c6acdc2124368f94efe110
- liveramp-site-verification=bLTcKGTyyCkVh8Zt5X8IYY9T4Uns9ZRoAEG6NPzTd-c
- pardot848313=94e68189fc6e698e53ab66f68f9fa66f68b14ab1837bac98f0a5b5b4dd57503d
- pardot1061392=f1c7431aa41d5e18d6f425faa7ee4bef2cc82af55471991546af317ad4988f6f
- v=spf1 include:_spf.samsung.com ~all
- cisco-ci-domain-verification=4d1fed540ceae17bd020e5d248bb657c382c66454d32a5984edd4871be659cea
- 8gv0n578hg7imelchsg2tesqq1
- dtm-domain-verification=5gAZbUOV4mzm7FcNMxN3Z_8Og_vvyqJh5FxCE_rh0zE
- globalsign-domain-verification=E636433F4A5B2209D29402CE4AE96D29
- google-site-verification=qKOICuq5bpeTBLMOeQs-pQ4fR4YdzZVLyFvahSDaRqc
- globalsign-domain-verification=BF9A67D3968C1D5FEC1440B12347B6AF
- pardot1061372=7f77a7e9d20bced708628f16f6245665a0b5d0ab840f492e5b8b9d0616ff8bff
- google-site-verification=gVlQpmwAi4l7c9YZ6vgGKB
- pardot880362=0579f4b1009200bd5629bc294b593112ab1438df4ebedf4de300d36b4a35e5bf
- pardot1123213=e21329a1ef7ab24c2a6a00afb2c9cdf6409a12ea19fd8c37c70c53eb8cbd3176
- globalsign-domain-verification=D4FBC243F3CA31BC63C84A1CE7856D69
- google-site-verification=XioIPzfjKziFDv7svS2vFxobJ1j6ApORgnD43-La5jc
- MS=ms51591264
- pardot1061382=ee554f6d1abf83530c2b3bd50be47bc5e417bb833dc9b2686e5c5c384d2e174c
- apple-domain-verification=1f6od6-lOUHNPseuv2qlLXryA-4aMi97KboxR65PVb0
- figma-domain-verification=fff7a09ce23c2d8329d368316712f1dcb0a29cb4c71a406f8f41dce4ef671081-1767768682
- dtm-domain-verification=sj6QpVm4qndJLuG0vmv2lv2WLlZ3g1EGLq9OItKaBQI
- google-gws-recovery-domain-verification=69734317
- box-domain-verification=b82590942dde67b52e8c41dc0e492a02ade277c5aede0e6de0b3b8de28a0085a
- docusign=022189ea-ba76-432a-abd7-19343970da7e
- docker-verification=a98547c5-d702-4b4b-9516-4331ed5171c8
- amazonses:GabQpmRJN86a4HQqoLu1IEu/b6hqbMTlQSHol1cVzhA=
- google-gws-recovery-domain-verification=57248779
- globalsign-domain-verification=d7cac74e387872153b45a1cf21f819ee
- samsung-domain-verification=9a471672-ab8b-442c-a646-b6fda8a9e698
- openai-domain-verification=dv-geyHaAZ2x2iRSG5mPLgCehBU
- google-site-verification=gVlQpmwAi4l7c9YZ6vgGKBrqIjduXkSx7ekuOPsOAlg
- globalsign-domain-verification=142A59A6E9D02E64F922A9C6893534A2
- miro-verification=16f39e2d161837f1d97cfb17ff7e81f243c68683
- cisco-ci-domain-verification=37f06378ba0e1526ad9a057438e3f2a1d0888e4e21d4ce75160ac7475679e080
- google-site-verification=Tb4utn-Cz0GYEzmsVzHfYhi6kv6XU--QYrYkfsVLwO0
- figma-domain-verification=74d791d52b49cbb05822c432d058f86bb47d2d97aa815d0ca470c6ef74a99003-1742422683
- pardot1005352=4bf1edcafe2d5f7ea48b1ab4c669194f7fb8492acec4617e4b3af673899d0f05
- globalsign-domain-verification=A931337188D2EF719A821F0016D8552E
- pardot1061362=d72ade8848a288815d8cd7fcdedf8e2ea1ffdf37f2e6199b9c6d2b118b260b11
- mongodb-site-verification=OK5ChSTjOEnRssN4ZNjB6y7xoqWBSraL
- canva-site-verification=Lz0E97jjjyiBnq4nGgrBzg
- asv=8c95d437a5f5281bf0b46412ea6410ff
- globalsign-domain-verification=9382b64f06fad76d1ebac344380ab28b
- atlassian-domain-verification=YJdK2oq4udj7wXxpQw52IsGEJue0ar/5JYtGr9lwcGNCffiKwPSGDZIQH0JlESij
- 7029addd-cf82-4d9e-9ac6-45cd3e47e467
Cloud / SaaS Services Detected
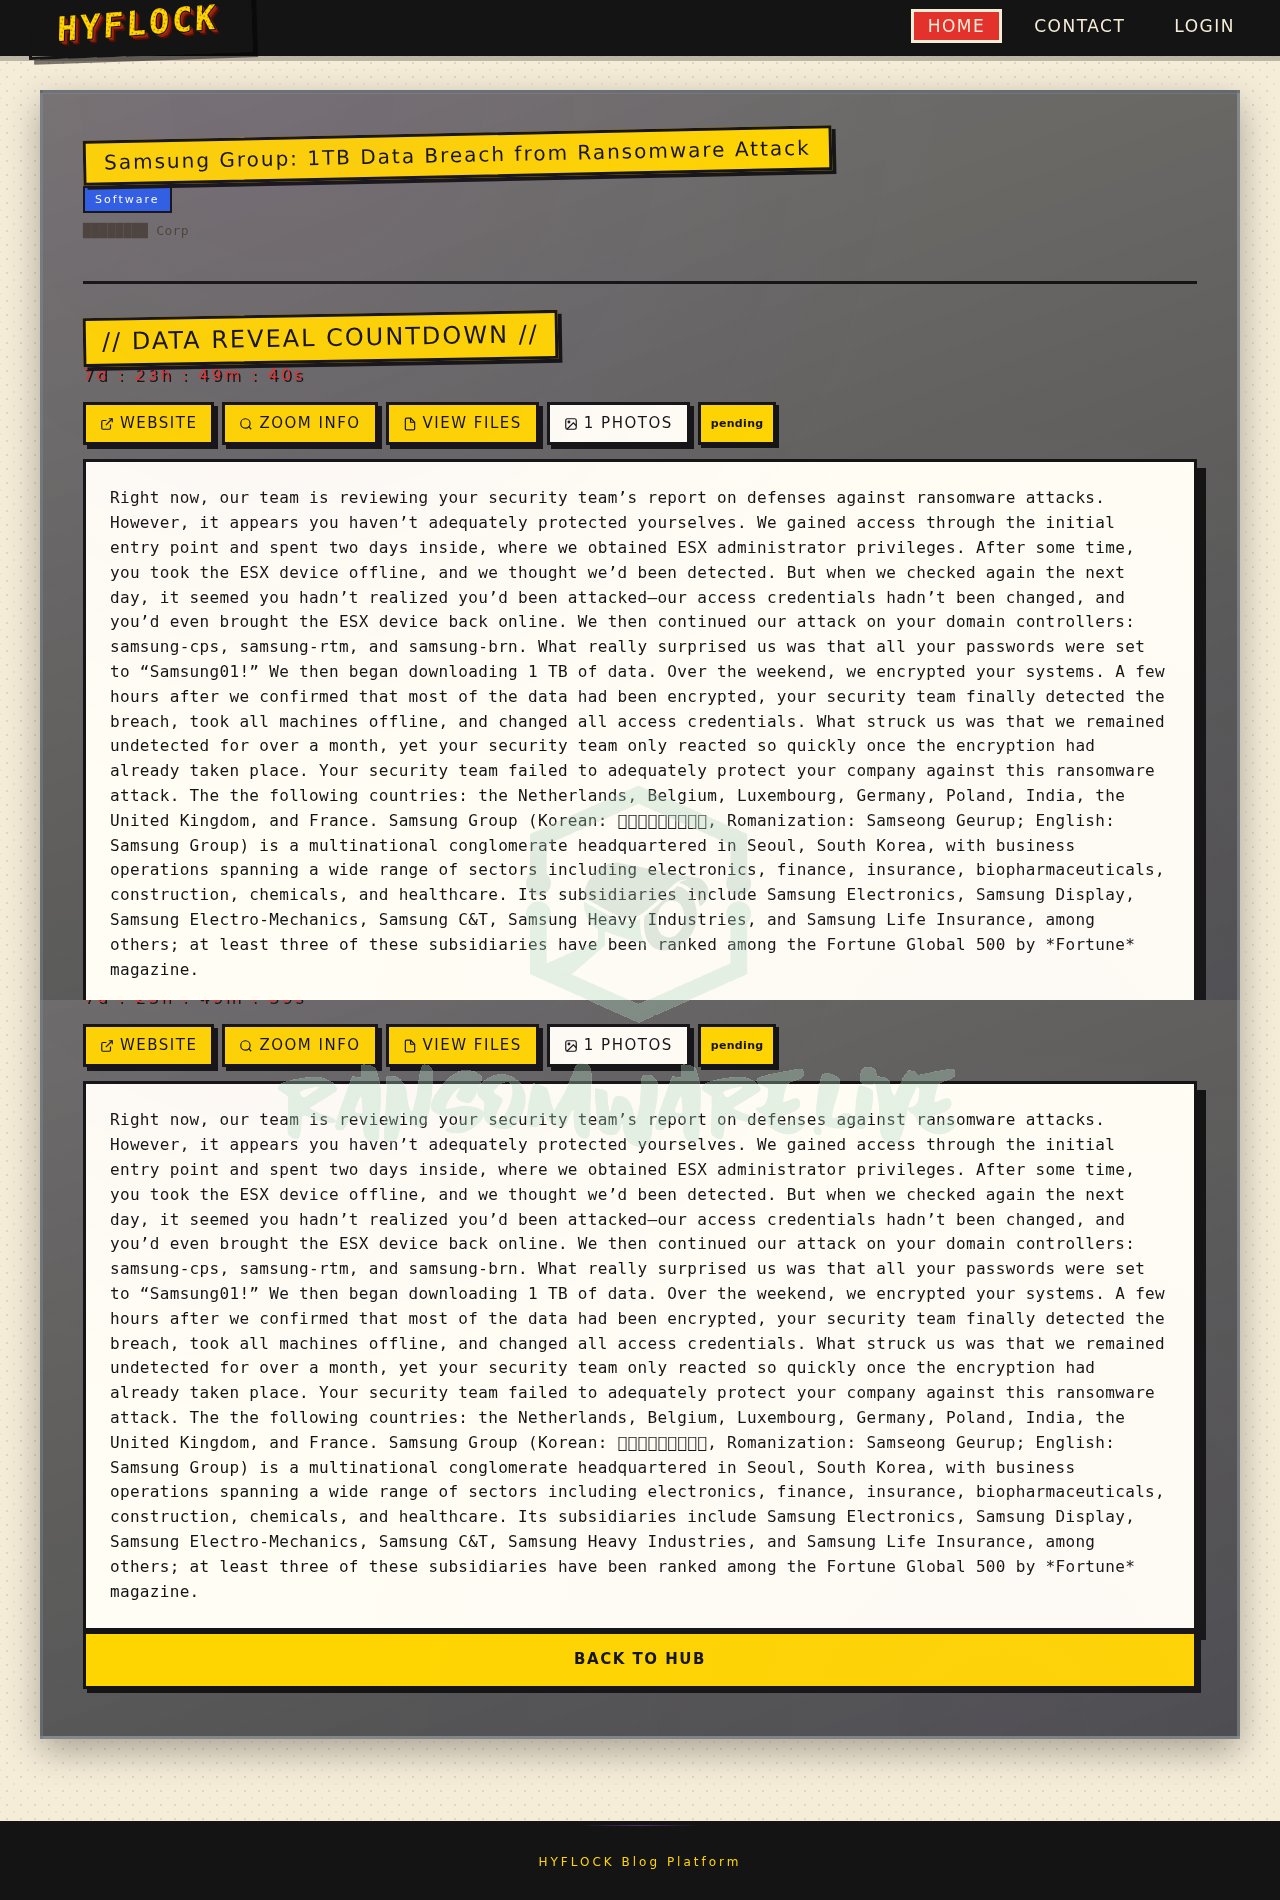
Leak Screenshot:
Other recent victims
Same group: Hyflock
-
 A Ransomware Attack on a Company Ranked Among the Top 30 in the Fortune 500
2026-11-22
-
 Data Breach at O&M University in the Dominican Republic
2026-11-22
-
 Dong Engineering Consulting Company Data Breach
2026-11-19
-
 Piz'wich Data Breach
2026-11-19
-
 An independent asset management firm in Casablanca
2026-11-18
Same sector: Technology
-
 persistent.com
2026-11-22
-
 F5A
2026-11-21
-
 PanLink
2026-11-21
-
 Marketech International
2026-11-21
Same country: Korea, Republic of
-
Samsung Electronics Co., Ltd.
2026-11-14
-
PANAX Group
2026-11-12
-
EMW
2026-11-10
-
MiraeING Co.
2026-11-10
-
JH Technology
2026-11-09
Legal Disclaimer: Ransomware.live does not engage in the acquisition, exfiltration, downloading, possession, hosting, access, consultation, redistribution, or disclosure of unlawfully obtained data. This platform indexes only publicly visible information posted by ransomware operators and open web sources without accessing or obtaining the underlying stolen content. The service is provided to support public awareness, legitimate research, and cyber-resilience. No stolen personal or confidential data is collected or distributed via this site.